

Summary
“Familiarity with API security” is a job posting’s way of saying “we didn’t check.” APIs sit under every model serving endpoint, every RAG pipeline, every tool calling agent, and 97% of the vulnerabilities in them can be popped with a single request, no login required. CASP doesn’t let anyone fake their way past that: six hours, live exploitation, real remediation, a report at the end, not a multiple choice quiz you can memorize on a lunch break. Cost to require it: $899. Cost to skip it and find out the hard way: $45K on a good day, north of $300K on a bad one, breach cleanup not included. That math isn’t subtle. It’s a rounding error wearing a “high risk decision” costume.
Every model-serving endpoint, every RAG pipeline, every agent that calls a tool, all of it runs over an API. Attack that layer and the AI theory underneath it never gets tested.
The data backs this up more than the industry’s AI-specific messaging suggests. A 2026 API ThreatStats analysis of over 67,000 published vulnerabilities found that 17% were API-related, and the breach data behind that number points to identity and access gaps, not novel attack classes.
Most of those gaps are trivial to exploit once found. The same report found that 97% of API vulnerabilities can be exploited with a single request, 98% are easy or trivial to exploit, and 59% require no authentication at all.
AI has made this worse, not different. In 2025 breach data, AI platforms and tooling accounted for 15% of all API-related breaches, tying software for the largest single category tracked.
IBM’s 2026 threat research points the same direction from a different angle. X-Force observed a 44% increase in attacks that began with exploitation of public-facing applications, driven largely by missing authentication controls, the same failure mode showing up in the API data.
Put plainly: a candidate who can recite the OWASP LLM Top 10 but has never secured an authenticated endpoint is prepared for half the job. The other half is the API surface underneath the model, and it’s the half most postings never verify.
Why AI Security Job Descriptions Miss the API Attack Surface
Open ten AI security job postings and the pattern repeats. Prompt injection gets a bullet point. Data poisoning gets a bullet point. Model theft gets a bullet point. The API that every one of those attacks actually travels through gets none.
That’s a real gap, not a technicality.
- An LLM doesn’t get attacked directly. It gets attacked through the endpoint that accepts input and returns output, which is an API by definition, governed by the same OWASP API Security Top 10 that predates the AI conversation entirely.
- A RAG pipeline exposes a retrieval endpoint, an embedding endpoint, and usually a vector database interface, three more API surfaces layered under the “AI” label, each carrying its own broken authentication, injection, and rate-limiting risks.
- An agent that calls tools is calling APIs. Insecure tool execution and excessive agency, both named in the OWASP Top 10 for Agentic AI Applications, are API security failures wearing an AI vocabulary.
- An MCP server exposing tools to an agent is an API surface with its own emerging risk list. Tool poisoning and shadow servers are access-control and input-validation problems, the same category API security has handled for a decade, just applied to a newer protocol.
- A model-serving platform, an inference endpoint behind a company’s own infrastructure, is functionally indistinguishable from any other backend API in terms of what secures it: authentication, authorization, rate limiting, input validation.
The market data backs up how large this blind spot actually is.
- The global application security market, which includes API security as a core segment, is forecast to reach $67.2 billion in 2026, up 15.5% year over year, according to a Q2 2026 market databook update.
- Growth in that market is explicitly attributed in part to AI adoption and expanding API ecosystems, the same two forces driving demand for the AI security roles these job postings are trying to fill.
- A 2026 analysis of API attack telemetry found AI platforms and tooling already account for 15% of API-related breaches, the largest single category tracked, which means the overlap between “AI security” and “API security” isn’t theoretical. It’s already the majority of the breach data.
- Practical DevSecOps’ own compensation research on this gap shows API Security Architects averaging over $180,000 in the US, with companies paying up to $190,000 for specialists, because the supply of people who can do the work hands-on, not just pass a theory exam, is thin.
A job description that lists adversarial ML concepts and never mentions authentication, authorization, or rate limiting is screening for half a threat model. The candidate who can name every item in the OWASP LLM Top 10 but has never secured an authenticated endpoint is prepared for the attacks that make headlines, not the ones that actually get exploited first.
The Certification That Closes This Gap: CASP
The Certified API Security Professional (CASP) validates the exact skill set your AI security engineer needs to secure model serving endpoints, RAG pipeline APIs, and agentic tool use interfaces.
Every one of those surfaces is, underneath its AI label, an API. CASP exists to prove someone can actually secure that layer, not just describe it.
What CASP verifies, framed as hiring criteria
Read this list as a checklist against your own posting, not as a course syllabus.
- Completed 9 hands on chapters covering API architecture, authentication and authorization attacks, the OWASP API Security Top 10, input validation, and REST, GraphQL, and SOAP security
- Practiced CI/CD pipeline integration and security automation, the same skill that lets a hire wire security scanning into a model serving deployment pipeline rather than bolt it on after the fact
- Worked through realistic attack scenarios including server side request forgery, broken authentication, broken access control, privilege escalation, and security misconfiguration, the same categories covered in this breakdown of top API security vulnerabilities
- Built the working knowledge to assess, audit, and secure APIs across the architecture styles a modern AI stack actually uses, not a single framework
Proof points to put in the posting
- A 6 hour practical, task based exam, not multiple choice: five challenges solved live, followed by 24 hours to write and submit a professional report, the same exam and certification process used across each of the ten credentials in this line
- Passing requires identifying, exploiting, and remediating real vulnerabilities, then documenting the finding the way an actual incident report would read
- 60+ browser based hands on labs, no VM setup, mirroring real attack scenarios rather than slide based theory
- A lifetime credential. No renewal fees, no re-examination cycle
That exam format is the part worth repeating to a skeptical hiring manager. A candidate who passed can walk through a specific challenge in detail. A candidate who only holds a multiple choice API security credential usually can’t get past a surface level description when asked the same thing, a gap laid out directly in this CASP comparison against a free MCQ based alternative: one tests recall, the other tests whether you can actually find and fix the vulnerability.
What CASP covers, mapped to what breaks in production
| Attack surface | What CASP verifies the candidate can do |
| Broken authentication and authorization | Identify and exploit flawed session, token, and permission handling on real endpoints |
| Injection attacks (REST, GraphQL, SOAP) | Find and remediate injection points across multiple API architecture styles |
| Server side request forgery | Recognize and defend against SSRF chains that pivot from an API into internal infrastructure |
| Rate limiting and resource exhaustion | Spot missing or misconfigured throttling before it becomes a denial of service path |
| Security misconfiguration | Audit deployment and gateway settings that leave an otherwise sound API exposed |
| CI/CD pipeline integration | Wire security scanning into a build pipeline rather than run it as a manual afterthought |
Why the trust signal carries weight here
The organization issuing CASP has trained 12,500+ professionals, and its certifications are trusted by organizations including Roche, Accenture, IBM, PwC, and Booz Allen Hamilton. CASP is also listed on the NICCS training catalog maintained by CISA, an independent confirmation beyond the issuer’s own marketing. For a hiring manager weighing an unfamiliar credential against a familiar one, that combination of enterprise adoption and a government catalog listing is what turns “never heard of it” into “already vetted.”
The number that justifies requiring it
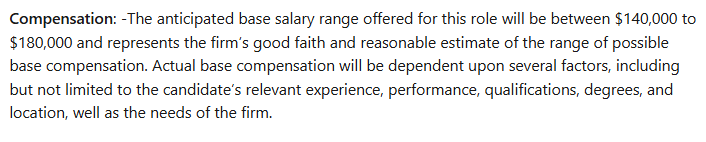
Research on this gap points to API Security Architects averaging over $180,000 in the US, with companies paying up to $190,000 for specialists who can close it. Against an $899 certification cost, that’s not a marginal ROI case. It’s a rounding error against what the role already pays once filled correctly.
For HR teams: Review the CASP certification and exam page before writing it into your next posting that touches production APIs.
For candidates: if the roles you’re targeting expose any kind of endpoint, model serving or otherwise, see CASP’s course structure and enrollment.
How to Write the Requirement Into Your Posting
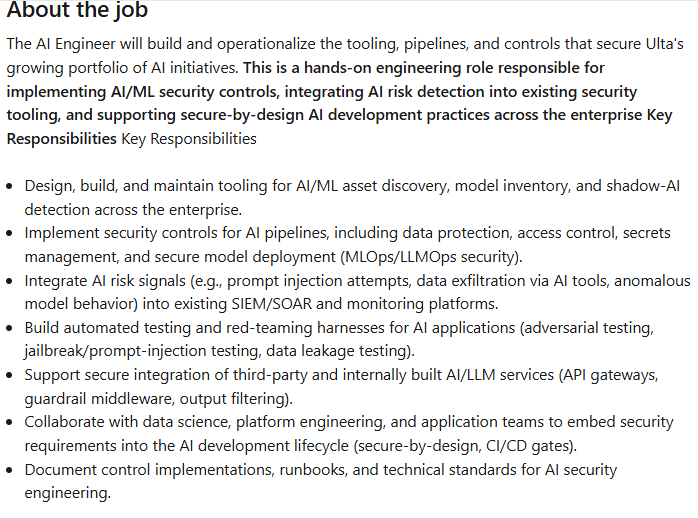
The template is short on purpose. A long, hedged certification line gives a recruiter room to skip it under time pressure. Use this directly:
“Required/Preferred: Certified API Security Professional (CASP) or demonstrated equivalent experience securing production API infrastructure.”
That second half matters. CASP is the fastest way to verify the skill, but it isn’t the only legitimate path into it. A candidate with years of hands on API security work, real incident response experience, or a comparable practical certification deserves a fair read too. The requirement is the skill, not brand loyalty to one credential.
Deciding required vs. preferred
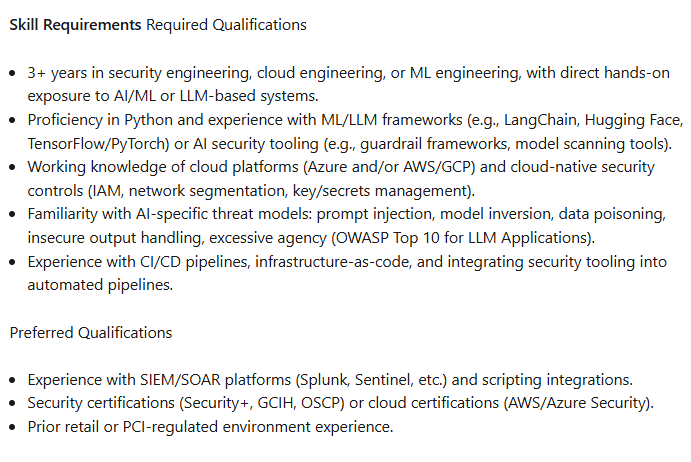
Ask one question: does this role touch production API infrastructure as a core responsibility, not a side task? If yes, make it required. If API security is one part of a broader mandate, preferred still filters better than leaving it out entirely.
- An AI Security Engineer or API Security Architect role: required. Securing endpoints, including the ones covered in the OWASP API Security Top 10, is the job description.
- A DevSecOps Engineer whose pipeline ships model serving or RAG endpoints: required, since the API layer is exactly what that pipeline exposes, and the same common API vulnerabilities apply whether the endpoint serves a model or a standard web app.
- A general AppSec Engineer at a company with a broader application surface, APIs among several: preferred.
- A role with no direct API ownership, purely policy or governance focused: skip it. Forcing an API security requirement onto a role that doesn’t touch the surface repeats the same mistake vague language makes, a requirement that doesn’t actually filter anything.
Key Responsibilities – Template
As a Senior DevSecOps Engineer, you will own security integration across our cloud-native platform, not just its performance and cost.
Automation, Site Reliability, and Cloud Operations
- Platform Engineering: Design, build, and maintain our core cloud-native platform infrastructure, with security scanning and gating built into the pipeline rather than added after deployment.
- Site Reliability: Design monitoring, logging, and tracing solutions that distinguish real security findings from noise, and own the alerting workflows that get incidents triaged and resolved quickly.
- Operationalize New Technology: Evaluate and integrate emerging tools, including AI-assisted platform capabilities, with a security review as part of that evaluation, not an afterthought.
- Cloud Governance and FinOps: Implement cost control strategies that don’t create security blind spots, including access and permissions reviews as part of any FinOps automation.
- System Architecture and Design: Participate in architecture discussions for new and existing cloud-native applications, with explicit ownership of authentication, authorization, and API security decisions at the design stage.
- Provide expert Field Support as the technical liaison for critical production issues, including security incidents traced to the API layer or CI/CD pipeline.
Required: Certified API Security Professional (CASP) or demonstrated equivalent experience securing production API infrastructure.
Preferred: experience integrating security scanning into CI/CD pipelines, and familiarity with AI or LLM security concepts if the platform includes model-serving or RAG components.
Pairing CASP with AI specific preferred qualifications
CASP proves someone can secure the interface. It doesn’t prove they understand adversarial machine learning or LLM specific attack patterns, and a posting that pretends otherwise misleads both the hiring team and the candidate. For roles where the model’s own behavior is part of the attack surface, layer AI specific qualifications on top as preferred, not required in place of CASP.
- Required: Certified API Security Professional (CASP) or demonstrated equivalent experience securing production API infrastructure
- Preferred: hands on LLM red teaming experience, including prompt injection testing against a live system, the kind of work covered in the OWASP Top 10 for Agentic AI Applications
- Preferred: familiarity with adversarial ML concepts such as training data poisoning, model theft, and evasion attacks
- Preferred: exposure to a recognized AI or LLM security framework, whether through a certification, a structured course, or documented project work, and where the role includes MCP servers or tool calling agents, familiarity with the OWASP MCP Top 10 specifically
This ordering does the honest thing. It sets the API security requirement as the floor every candidate must clear, since that’s the layer every model serving, RAG, or agentic system runs on regardless of how sophisticated the AI specific attack surface gets. The AI specific line then becomes the differentiator among candidates who already cleared that floor, which is a more accurate reflection of how these roles actually fail: not because someone lacked adversarial ML theory, but because nobody checked whether they could secure the endpoint underneath it.
Where the requirement sits in the posting
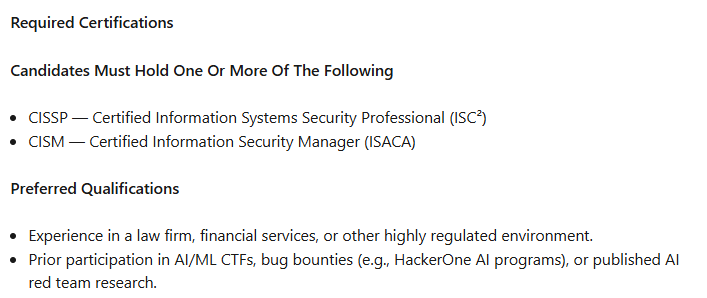
Put the CASP requirement in the qualifications section and repeat it once in the summary paragraph if your posting has one. Applicant tracking systems weigh the opening lines of a description more heavily than a bullet buried six paragraphs in, so a requirement stated only once, late, gets less algorithmic and human attention than the same line stated early.
| Role type | CASP requirement | AI specific qualification |
| AI Security Engineer, model serving in scope | Required | Required |
| API Security Architect | Required | Not applicable |
| DevSecOps Engineer, AI workloads present | Required | Preferred |
| General AppSec Engineer, broad surface | Required | Not Listed |
| Governance or policy focused role | Not Listed | Not Listed |
Verifying the requirement once an application comes in
Don’t stop at the resume line. The exam and certification process behind CASP produces a verifiable credential, and candidates should be asked to include a link to it, the same way earlier sections in this guide recommend for AI specific certifications. It takes a recruiter under a minute to confirm, and it separates a candidate who did the work from one who lists a skill they read about once.
Verifying the Certification Before You Trust It
A certification name on a resume is a claim. Whether that claim means anything depends on what it took to earn it, and that’s checkable in a few minutes if you know what to look for.
What to check
Renewal structure: a credential with no renewal cycle and no ongoing fees signals the issuer expects the skill to hold up over time, not a subscription built around recurring exam fees
Exam format: is it a live, practical exercise against a real system, or a set of multiple choice questions answered from memory
Time under evaluation: does the exam run for hours under exam conditions, or can it be completed in a sitting with no real time pressure
What passing actually requires: finding and fixing a real vulnerability and writing it up, or selecting the correct answer from four options
Issuing body reputation: is the certification listed on an independent catalog such as NICCS, maintained by CISA, rather than relying only on the issuer’s own claims.
Public verification: does the issuer provide a way to confirm the credential independently of the resume line it appears on
Why CASP’s exam format is the stronger signal
CASP’s exam and certification process requires five task based challenges solved live across 6 hours, followed by 24 hours to write and submit a professional report. That is a materially different bar than a multiple choice format, and the difference shows up the moment you ask a candidate to describe what they did.
A candidate who passed a practical exam like this can walk through a specific challenge: what the vulnerability was, how they found it, what the fix looked like, and what they wrote in the report to explain it. A candidate who passed a credential mill’s multiple choice exam usually can only restate definitions, because that’s all the exam ever tested.
This is the same distinction laid out directly in a comparison between CASP and a free, multiple choice based alternative: one exam tests whether a candidate can recall API security concepts, the other tests whether they can find and fix the vulnerability in front of them. Multiple choice can be studied for in a weekend. Live exploitation and remediation cannot be faked the same way, because the system either gets secured or it doesn’t.
A quick reference for the checklist above
| Signal | Practical exam (CASP) | Credential mill certification |
| Format | Live exploitation and remediation, 5 tasks in 6 hours | Multiple choice questions, no live system |
| What a pass proves | Working ability to find and fix real API vulnerabilities | Recall of terms and definitions |
| Time to prepare a fraudulent pass | Difficult, requires real lab time and skill | A weekend of memorization |
| Independent listing | Listed on the NICCS training catalog | Often absent from any independent index |
| Renewal cycle | None, lifetime credential | Frequently required annually, sometimes with low effort |
| What a candidate can describe afterward | Specific challenge, specific fix, specific writeup | Vague generalities |
The one step that closes the loop
Ask for the credential link, not just the name on the resume. A verifiable badge, checked against the certification page itself, turns a claim into a confirmed fact in under a minute, the same verification standard this guide applied earlier to AI specific certifications. A resume line is trust. A verified link is proof, and proof is the entire point of requiring a credential in the first place.
The ROI Case for Making This a Requirement
Most ROI arguments for a certification requirement lean on a table: mis-hire cost here, certification cost there, done. That’s useful, but it hides how the cost of skipping this specific requirement actually plays out. Here’s the same case walked through as a timeline instead, because a mis-hire in an API-exposed AI role doesn’t cost money all at once. It costs money in stages, and each stage compounds the one before it.
Month one through three: the gap is invisible
An unqualified hire in this role looks fine at first. They can talk about the architecture, describe the pipeline, and pass a standard technical interview built around general DevOps or AppSec questions. Nothing in a typical onboarding process forces them to demonstrate live exploitation and remediation skill, the exact thing a practical exam like CASP’s tests and a resume can’t.
This is the period where the cost is entirely invisible, and it’s also the period where a company convinces itself the hire is working out.
Month four through eight: the gap starts showing up in the work
Slower triage is usually the first visible symptom. A scanner flags a finding, and the hire either can’t tell if it’s a real vulnerability or noise, or takes several times longer than a verified specialist would to confirm it. Multiply that delay across every finding a model serving or RAG endpoint generates, and the security team’s actual throughput drops even though headcount looks fine on paper.
This is also the stage where a genuinely exploitable gap has the longest window to sit open. Research on this exact surface found that 97 percent of API vulnerabilities can be exploited with a single request, and 59 percent require no authentication at all, according to a 2026 analysis of over 67,000 published API vulnerabilities. Every month a gap like that goes unaddressed because the person responsible for finding it can’t reliably do so is a month the exposure compounds, not a month it holds steady.
Month nine and beyond: the cost becomes visible, and expensive
Two things tend to happen around this point, and either one alone justifies the certification requirement retroactively.
- A breach or near miss surfaces the gap directly. Gartner’s research on this surface found that the average API breach leaks at least 10 times more data than the average security breach, which means remediation, disclosure, and customer notification costs scale with the exposure itself, not with what the company paid the hire.
- An audit finds it first. A missed vulnerability class or a misconfigured pipeline gate becomes a documented finding tied to a specific hiring decision, and the compliance exposure that follows is harder to walk back than a breach, because it’s now a paper trail.
Either path leads to the same decision: replace the hire, backfill the role, and absorb the cost of everything that happened in between.
The other path
Compare that timeline to what requiring a verified CASP credential at the point of hire actually costs: $899, paid once, with no renewal fee attached to it. The exam that produces it takes 6 hours of live exploitation and remediation work, the same skill the mis-hire timeline above shows breaking down slowly over eight months instead of getting checked once on day zero.
There is no month four in this version of the story where triage quietly slows down, because the skill was verified before the offer went out rather than discovered by accident during an incident. The $899 doesn’t replace good judgment in the rest of the hiring process. It replaces the eight months of invisible risk that a resume alone can’t rule out.
Why this argument works from both directions
An HR team reading this timeline gets a concrete answer to why the requirement belongs in the posting before the first application comes in, not after a bad hire six months in. A candidate reading the same timeline gets an equally concrete answer to why the $899 and a weekend of lab time are worth it: it’s the difference between being screened out at month zero for lacking a skill you can verify in a weekend, or getting hired into a role where that same gap surfaces slowly, expensively, and with your name attached to it.
Final Thoughts
A resume line claiming API security skill is a guess dressed up as a qualification. A verified CASP credential is proof, checkable in under a minute, backed by a six hour exam that can’t be memorized over a weekend.
The timeline makes the case better than any single number could. Month zero is where the decision gets made, either verify the skill before the offer goes out, or find out eight months in when triage slows down, a finding gets misjudged, or an auditor traces a gap back to a hiring decision nobody checked. One path costs $899. The other costs $45,000 at the floor, over $300,000 at the ceiling, and that’s before a single breach or compliance finding gets added on top.
That comparison isn’t close, and it doesn’t need more evidence to make the case. It needs a decision.
If you’re hiring: Stop posting “API security experience preferred” and start requiring proof. Review the CASP certification and exam page right now, and write the requirement into your next posting before another unverified resume gets past your screen.
If you’re job hunting: Don’t wait for a rejection to tell you the gap existed. Enroll in CASP today, pass the six hour practical exam, and walk into your next application with a credential a recruiter can confirm in under a minute instead of a claim they have to take on faith.
Either way, the decision is the same size: $899, made once, against a cost that only grows the longer it waits.
FAQs
No. Pair it with AI and LLM specific security requirements. CASP validates API security expertise, which is the delivery layer for most AI system attacks, but it doesn’t cover adversarial ML techniques like data poisoning or model extraction on its own. Treat it as the required baseline, not the whole requirement.
CASP costs $899. A quick note on the justification: the widely repeated claim that 94 percent of web breaches originate at the API layer doesn’t trace back to a verifiable independent source, so it’s worth leaving out of your own posting. The numbers that do hold up are strong enough on their own. A 2026 analysis of over 67,000 published API vulnerabilities found 97 percent can be exploited with a single request and 59 percent require no authentication at all, and companies are reportedly paying up to $190,000 for specialists who can close this exact gap. Against that risk, an $899 one time certification cost is a rounding error.
A six hour practical, task based exam requiring candidates to identify, exploit, and remediate real API vulnerabilities across REST, GraphQL, and SOAP architectures, then write a professional report. It’s not a multiple choice knowledge check, and that distinction is what makes the credential worth verifying rather than taking on faith.
Consider preferred rather than required for junior roles, and required for mid to senior roles where the candidate is expected to own API security decisions independently. A junior hire growing into the role can earn the certification on the job. A senior hire making unsupervised calls about production API exposure should already have it.
Yes. It’s issued by an organization that has certified over 12,500 professionals and is trusted by organizations including Roche, Accenture, IBM, PwC, and Booz Allen Hamilton. CASP is also listed on the NICCS training catalog maintained by CISA, an independent confirmation beyond the issuer’s own marketing. Both are worth citing directly in the posting to signal you know what you’re asking for.
Yes, and it’s often the faster path. Pairing an existing security engineer’s CASP certification with targeted AI and LLM security training can be quicker and cheaper than an external senior hire, especially given how thin the external candidate pool is for roles that require both skill sets at once.