

Summary
A Cybersecurity AI Forward Deployed Engineer secures AI agents inside a client’s live systems, with real credentials attached. Accenture pays up to $235,100 for this role. You need deep security experience, hands-on agentic AI skills, and proof you can own results inside someone else’s environment. This guide covers the pay data, the skills employers test for, and the 6-step path to get there along with latest certification details
A Cybersecurity AI Forward Deployed Engineer works inside a client’s company and secures AI agents running in production, with real credentials and real access attached. Accenture now hires for this exact title, with US pay listed as high.
The job needs deep security skill, hands-on experience deploying agentic AI, and ownership of outcomes inside someone else’s environment. Here’s the real path: the job data, the pay numbers, and the skills employers screen for.
What is a Cybersecurity AI Forward Deployed Engineer?
Palantir made the Forward Deployed Engineer title well known. These engineers work at a client’s site, building and deploying software inside real, messy environments. A product team ships features from head office. A forward deployed engineer ships them from inside the client’s world. Add “cybersecurity AI” to the title, and the job narrows fast.
Accenture’s own posting puts the role deep inside production delivery. The engineer sits with a client’s security and engineering teams and owns results: a smaller attack surface, safer AI in production, and a measurable jump in security posture.
Two details set this apart from a standard security job:
- Agentic coding tools such as Claude Code, Cursor, and GitHub Copilot are the primary way this work gets built.
- You need hands-on production experience deploying agentic AI. Lab work and coursework don’t count. Accenture calls this non-negotiable.
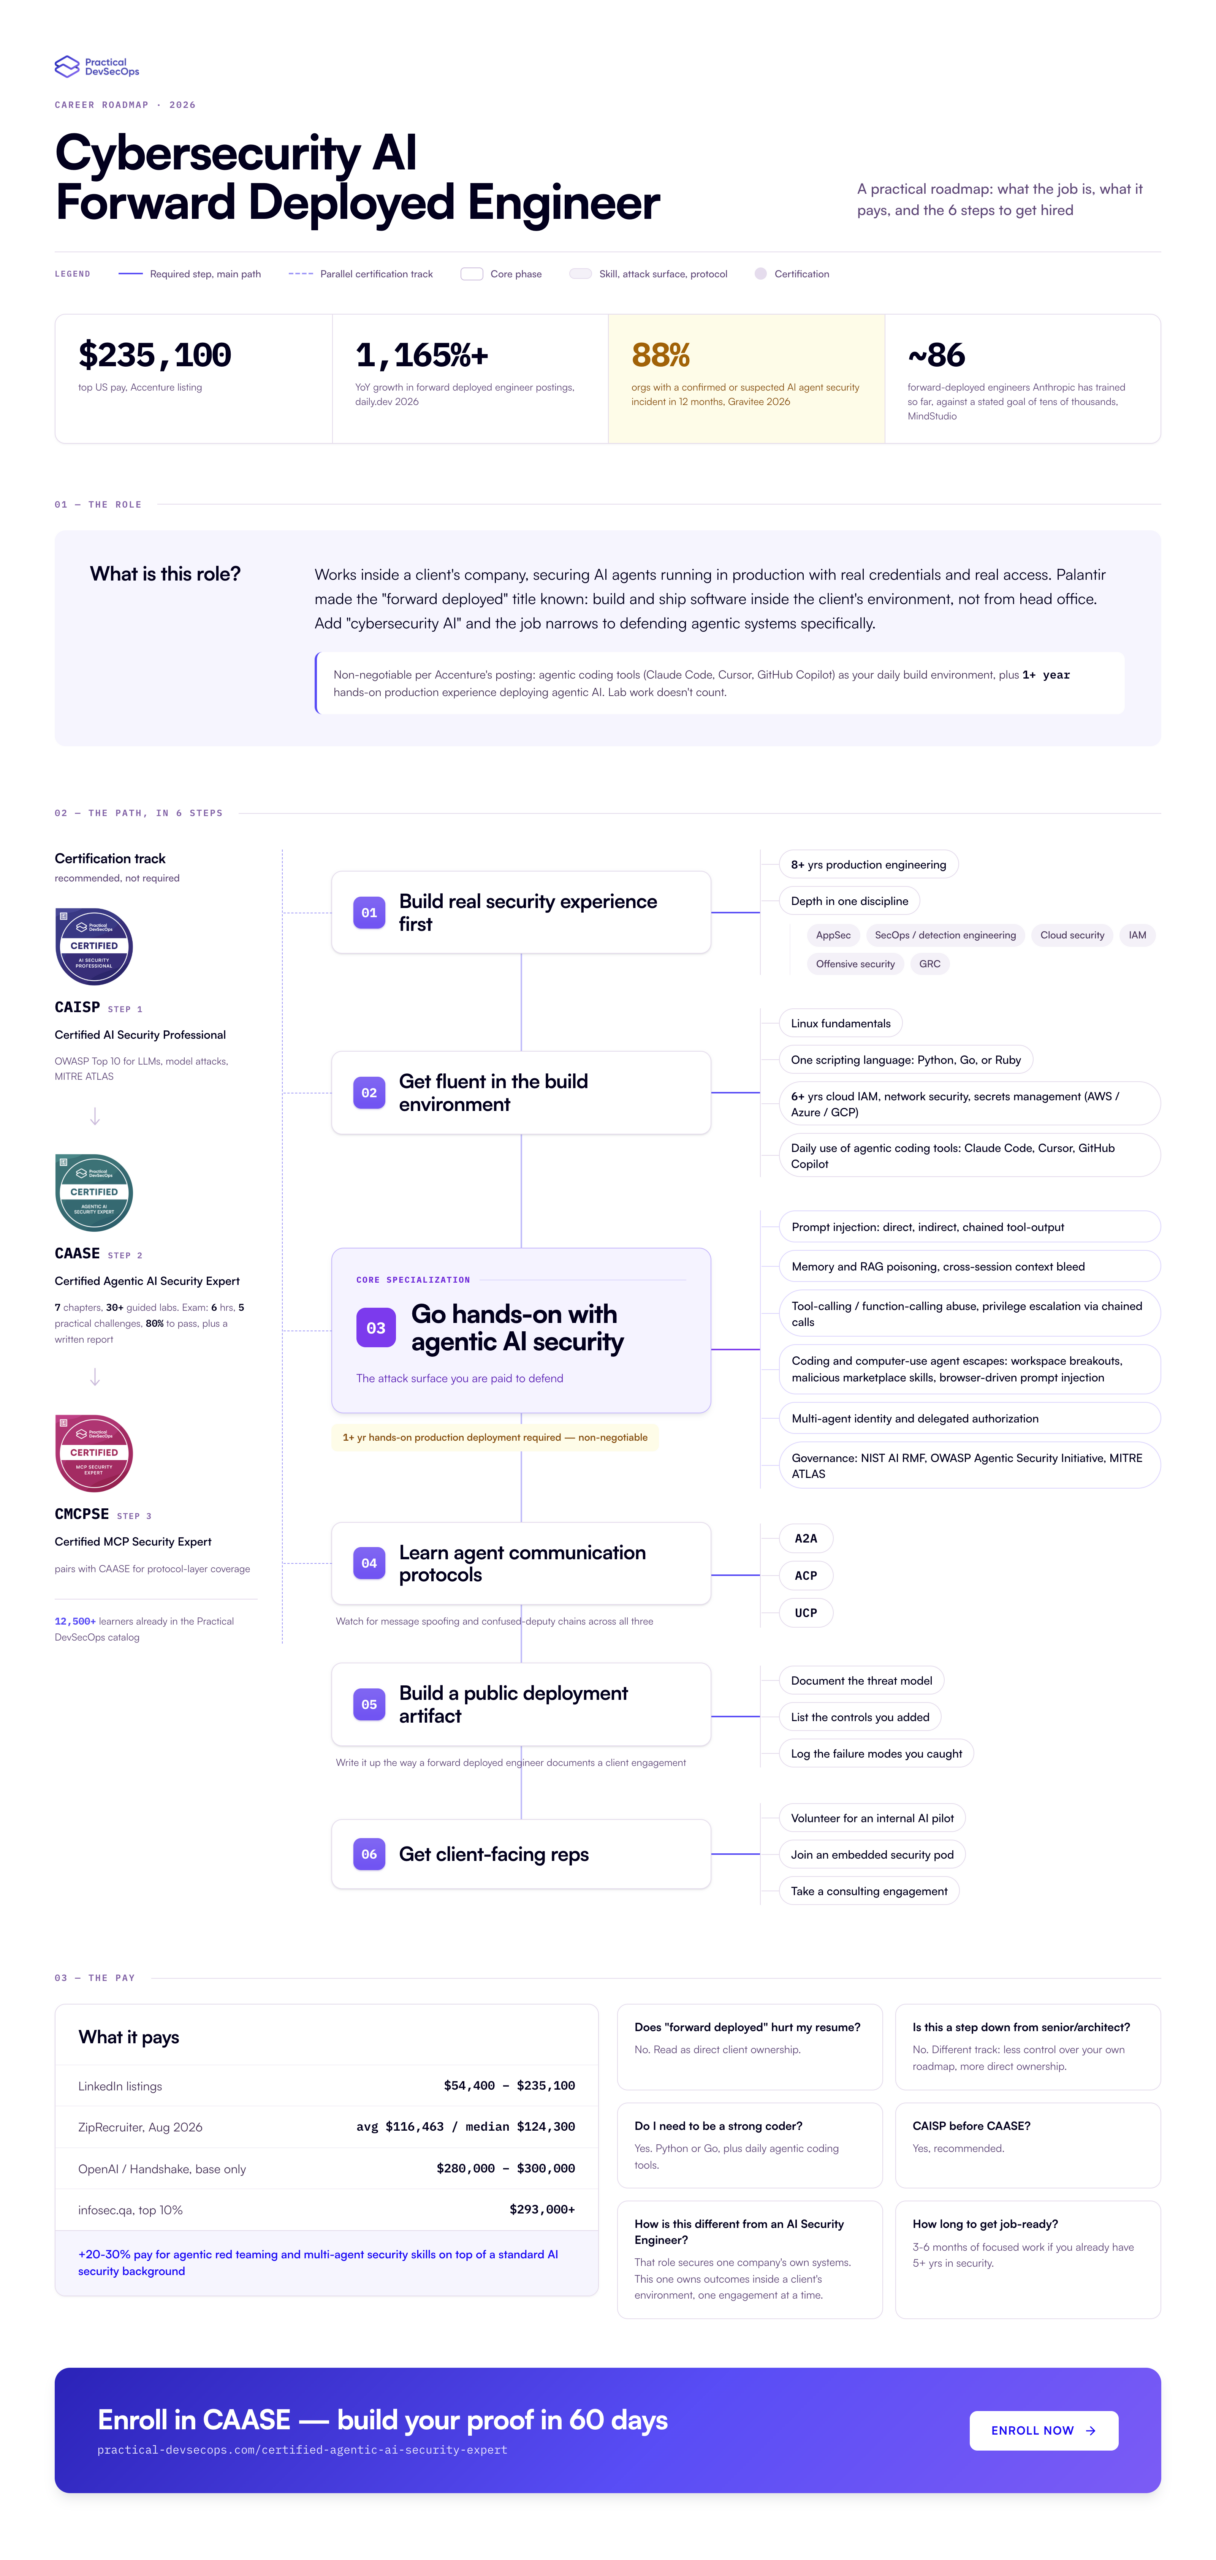
Cybersecurity AI Forward Deployed Engineer Roadmap
Why did this job appear now?
Because AI agents already broke things. 88% of organizations confirmed or suspected an AI agent security incident in the past 12 months. Healthcare hit 92.7%. Financial services hit 54.7%, per Gravitee’s State of AI Agent Security 2026 report. Agents now run with real credentials and real database access. Most companies deployed them faster than they built the controls to watch them.
Forward deployed engineer job postings are climbing fast too. They grew more than 1,165% year over year, according to daily.dev’s 2026 roundup.
Anthropic said it planned to train tens of thousands of forward-deployed engineers to help banks, airlines, and insurers deploy AI. It reportedly trained around 86, per MindStudio. That gap between demand and supply is why these jobs pay so well right now.
How much does a Cybersecurity AI Forward Deployed Engineer make?
Pay varies by employer, seniority, and how much of the agentic AI security stack you know cold.
| Source | Role | Pay range (USD) |
| LinkedIn listings | Cybersecurity AI Forward Deployed Engineer | $54,400 – $235,100 |
| ZipRecruiter, Aug 2026, via KDnuggets | Forward Deployed Engineer, general (avg / median) | $116,463 / $124,300 |
| OpenAI, Handshake, via MindStudio | Forward Deployed Engineer, base only | $280,000 – $300,000 |
| infosec.qa, 2026 | AI Security Engineer, top 10% | $293,000+ |
Add agentic red teaming and multi-agent security skills to a standard AI security background, and pay jumps 20 to 30% higher, per infosec.qa’s guide. Agentic AI security knowledge is now the biggest pay multiplier on a cybersecurity resume. It’s a big reason AI security engineers already clear $200K in the US.
What skills does a Cybersecurity AI Forward Deployed Engineer need?
Accenture’s hiring bar for this role is specific and steep. You need:
- 8+ years of engineering experience in production environments
- Depth in one security discipline: AppSec, SecOps/detection engineering, cloud security, IAM, offensive security, or GRC
- At least 1 year of hands-on experience deploying agentic AI in production (lab work doesn’t count)
- 6+ years with cloud IAM, network security, secrets management, and AI service configuration on AWS, Azure, or GCP
- Daily fluency with agentic coding tools as your default build environment
That covers the engineering side. The part most career guides skip is the agentic AI attack surface itself.
The agentic AI attack surface you’re paid to defend
- Prompt injection across direct, indirect, and chained tool-output vectors
- Memory and RAG poisoning, plus cross-session context bleed
- Tool-calling and function-calling abuse, including privilege escalation through chained calls
- Coding and computer-use agent escapes: workspace breakouts, malicious marketplace skills, browser-driven prompt injection
- Multi-agent identity, delegated authorization, and protocol-level attacks across A2A, ACP, and UCP
- Governance work: NIST AI RMF, the OWASP Agentic Security Initiative, MITRE ATLAS
Most cybersecurity training stops at prompt injection against a single model. This role goes several layers deeper: memory stores, tool orchestration, agent-to-agent trust. Structured, hands-on training closes that gap faster than piecing it together from scattered blog posts and vendor docs.
The 6-step roadmap to become a Cybersecurity AI Forward Deployed Engineer
Follow these 6 steps in order.
- Build real experience in one security discipline first:
Accenture wants 8 years of engineering plus depth in AppSec, cloud security, IAM, offensive security, SecOps, or GRC. There’s no shortcut around this. - Get fluent in Linux basics and one scripting language:
Python, Go, or Ruby. Agent runtimes and MCP tooling assume you can read and write scripts on your own. - Go hands-on with agentic AI security specifically:
Build and break a real agent runtime: poison its memory, hijack its goal mid-task, escalate privilege through chained tool calls. This is where most candidates fall short, because the skill barely existed 18 months ago. - Learn agent communication protocols:
A2A, ACP, and UCP govern how agents delegate tasks and share context. Attacks against these protocols, including message spoofing and confused-deputy chains, are already showing up in real deployments. - Build a public deployment artifact:
Document a real agent you secured: the threat model, the controls you added, the failure modes you caught. Treat it the way a forward deployed engineer treats a client engagement. - Get client-facing reps:
Volunteer for an internal AI pilot, join an embedded security pod, or take a consulting engagement. The title says “forward deployed” for a reason. You need proof you can own outcomes inside someone else’s environment.
Why Practical DevSecOps Certified Agentic AI Security Expert (CAASE) training is different?
Most AI security training on the market teaches prompt injection against a chatbot and calls it done. Certified Agentic AI Security Expert (CAASE) goes several layers deeper: attacking and defending an agent’s reasoning loop, memory, tool-calling interfaces, multi-agent identity, and communication protocols, across 7 chapters and 30+ guided labs.
Three things set it apart from normal AI security courses:
- The exam is a hands-on job simulation. You get 6 hours and 5 practical challenges, need 80% to pass, then submit a written report, the same way you’d document a real client engagement.
- It covers the specific stack this role screens for, including MCP tool-calling abuse, A2A/ACP/UCP protocol attacks, and AI Bill of Materials generation, topics that generic LLM security courses skip entirely.
- It’s part of a full AI security certification track. CAASE builds on Certified AI Security Professional (CAISP) and pairs with Certified MCP Security Expert (CMCPSE), giving you a hands-on path across the model, protocol, and agent layers.
If you want a forward deployed engineer certification with a real cybersecurity focus, CAASE fills that gap. Sign up and start building that proof today, alongside 12,500+ learners already in the Practical DevSecOps catalog.
Conclusion
The Cybersecurity AI Forward Deployed Engineer role didn’t exist 2 years ago. Now Accenture pays up to $235,100 for it, and demand already outpaces supply. You close that gap with real security depth, hands-on agentic AI skills, and proof you can own outcomes inside a client’s environment. Enroll in the Certified Agentic AI Security Expert (CAASE) course and build that proof in 60 days.
FAQs
No. Hiring managers read “forward deployed” as direct client ownership. On teamblind’s engineering community, engineers describe it as a sideways move at worst, with real customer exposure most engineers never get.
No. It’s a different track. You trade some control over your own roadmap for direct ownership of a client’s outcomes, and the pay reflects that trade.
Yes. You need enough Python or Go to read and modify agent runtimes and MCP tooling, plus daily fluency in agentic coding tools. Accenture treats those tools as your main way to build software.
Practical DevSecOps recommends it. Certified AI Security Professional (CAISP) covers AI and LLM security fundamentals: the OWASP Top 10 for LLMs, model attacks, and MITRE ATLAS. Certified Agentic AI Security Expert (CAASE) builds on that foundation and moves into the agentic layer: runtimes, memory, tool orchestration, and multi-agent systems. If you’re still deciding where to start, see how CAISP compares against Certified MCP Security Expert (CMCPSE), the other certification in the same track.
An AI Security Engineer usually secures one company’s own AI systems from the inside. A Cybersecurity AI Forward Deployed Engineer works inside client environments, one engagement at a time, owning security outcomes for systems they don’t fully control. This role demands more client-facing skill and wider range across tech stacks.
If you already have 5+ years in a security discipline, plan on 3 to 6 months of focused, hands-on agentic AI security work to close the gap. Follow a structured plan, like this guide on how to prepare for an AI security certification. If you’re earlier in your career, build that security depth first. There’s no shortcut past that requirement.